Put an approval gate in front of your AI agent in 5 minutes.
Claude (desktop or claude.ai), Cursor, Meta Muse, Grok Bot or the agent you built: point it at Guardyx AI and every tool call is checked against your rules before it runs. Risky ones wait for you. Every decision is on a hash-chained record.
Every AI action passes through Guardyx.
Free: 5,000 tool calls a month through Guardyx, every governance feature, connectors included. No card, no expiry.
Approval requested
Held for a human before it runs.
- Agent
- Claude Desktop
- Tool
GMAIL_SEND_EMAIL
Agent's stated reasonUnverified
You asked me to tell customers about the new Q3 pricing, so I’m emailing the full customer list.
Arguments
{
  "to": "ALL-CUSTOMERS@list.acme.com",
  "body": "Effective immediately, new Q3 pricing…"
}
Policy
Bulk external email to a distribution list: approval required.
Approved. The email runs now, and your decision is on the audit trail.
Denied. The email never left, and your decision is on the audit trail.
Your AI agents aren't just chatting anymore.
Claude, Cursor, and the agents you build now act with your credentials, faster than you can read what they'll do.
If your agents only draft text and never call a real tool, you probably don't need this yet.
Still weighing it up?
It only takes one.
- Force-push over your main branch.
- Email everyone in your contacts.
- Delete files or a table you still needed.
- Paste a secret key somewhere public.
- Spend money with your card or API credits.
- Cancel a meeting with your biggest customer.
Each happens in seconds, under your name, and you only find out afterward.
One gate for every agent you run.
Point every agent and MCP client at Guardyx. One control point, one record.
Your agents
- Claude (desktop or claude.ai)
- Cursor
- Meta Muse
- Grok Bot
- ChatGPT (over MCP)
Guardyx
Policy, approvals, audit
hosted, or in your VPC
The systems they act on
- Sales & email tools
- Payments & ledgers
- Code & repos
- Production infrastructure
- Internal data & records
Connect your MCP clients.
Every client above signs in over OAuth 2.1, except ChatGPT, which connects directly. No adapter needed.
Connectors included.
Guardyx hosts the connectors and governs them. One bill, no separate connector subscription, no agent code to change.
Bring the agents you already run.
Native adapters for CrewAI, AutoGen, Google ADK, the OpenAI and Anthropic agent SDKs, and LangGraph, with LangChain tools governed through that same LangGraph adapter.
Control at the moment of action.
Not a log you read afterward. The decision happens before the action runs.
Your agent proposes
GMAIL_SEND_EMAIL
to every customer on a list
Guardyx
Checks it against your policy
before anything runs. If the check fails, nothing runs.
Allowed
In policy, so it runs now.
Held
Waits for a human to approve.
Denied
Never reaches the system.
Audit trail
Every decision recorded
hash-chained, including the ones that never ran.
Fails closed.
Guardyx fails closed by default: if the policy check cannot complete, the action does not run.
Keeps the receipts.
A hash-chained, tamper-evident record of what was allowed, held or denied.
Runs where you need it.
Hosted, or self-hosted in your own VPC or on-prem.
No code in your agent.
The gate lives in Guardyx, not in your agent loop. Approvals work for any MCP client the day you connect it.
This is the screen you'll use.
The real approvals queue: risky tool calls held before they run.
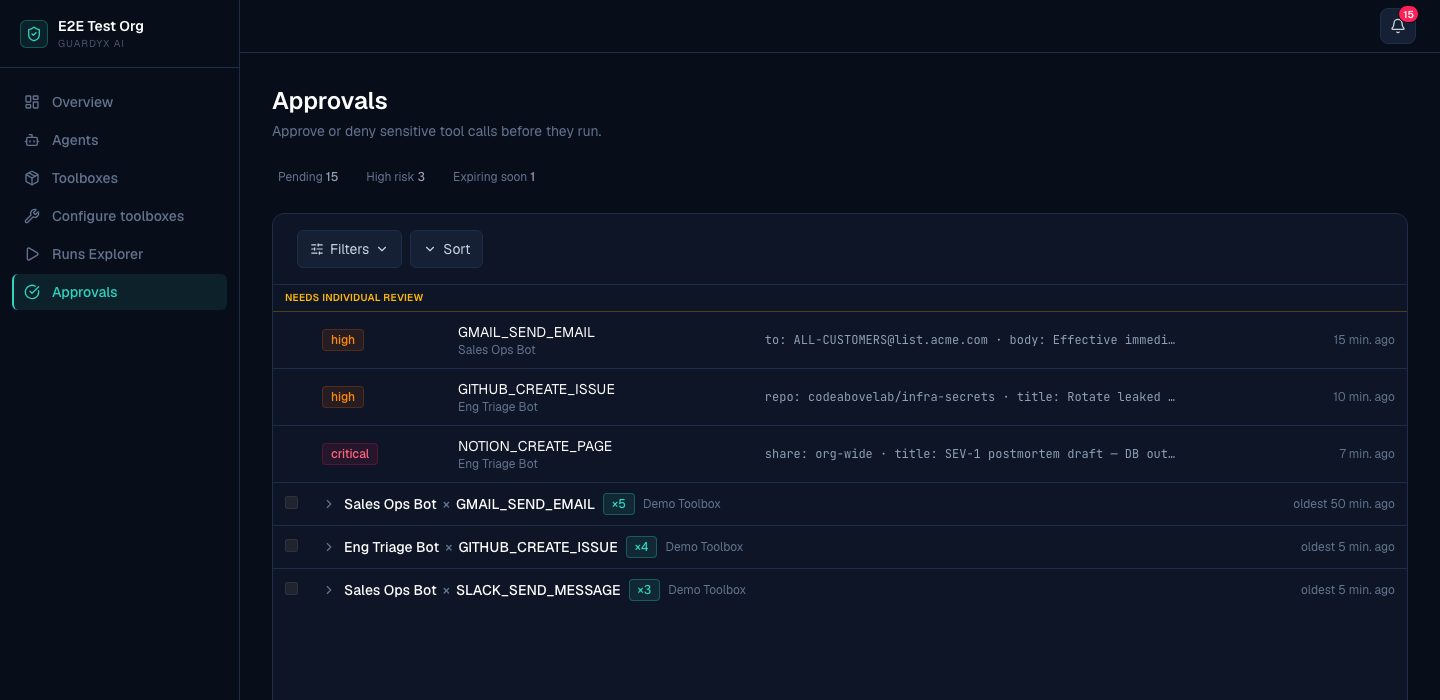
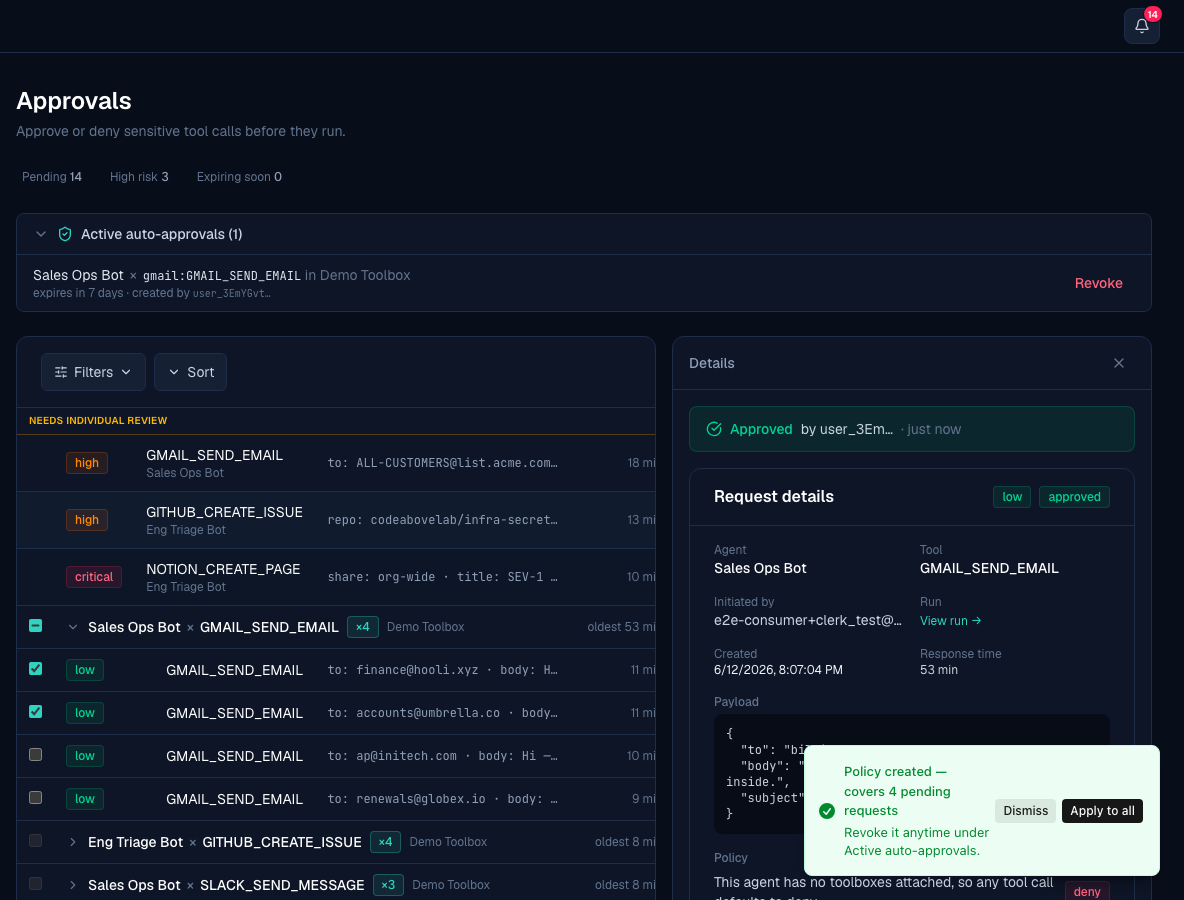
Open a held action, see why it stopped, approve or deny.
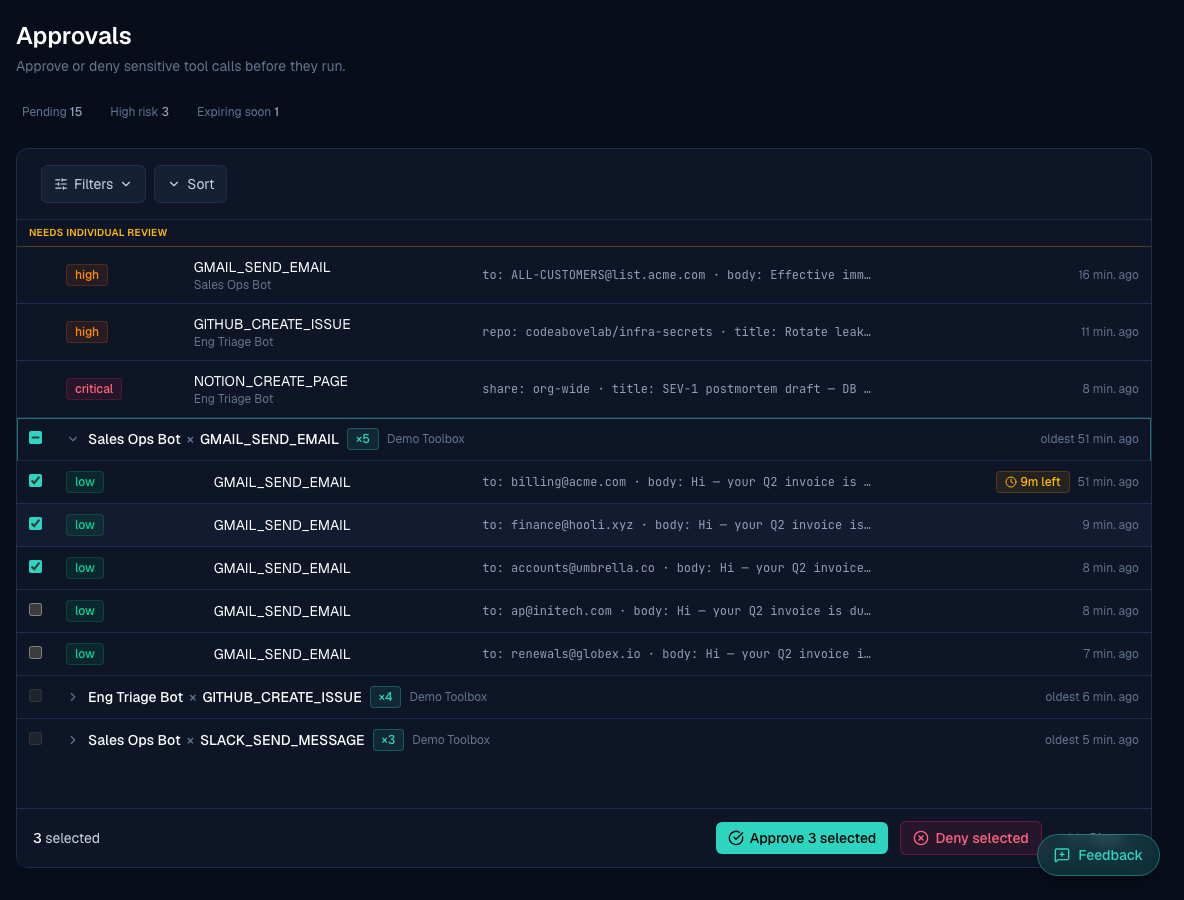
Clear routine actions in one batch.
Prevent. Review. Prove.
Nobody wants to be the person explaining why an agent did something nobody approved. Guardyx does all three jobs, on every action.
Prevent
No risky action runs without a policy decision.
Intercept the action and check it against your policy.
Review
You see only what matters.
Hold the exceptions for your sign-off; let routine work through.
Prove
Export the evidence when you need it.
Run it, and log the decision as tamper-evident proof.
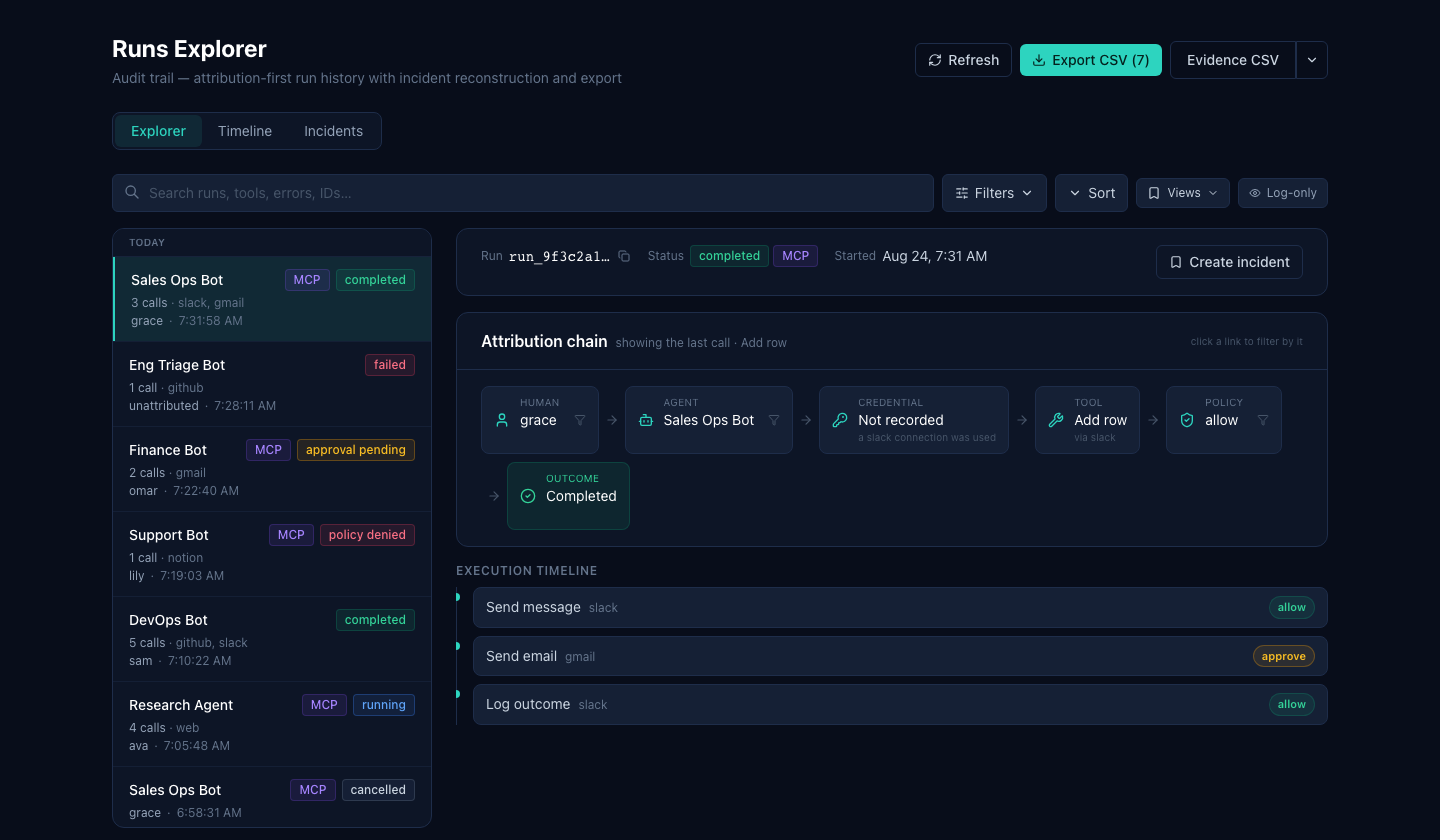
What your agent actually did last week: every run, every decision, exportable as a hash-chained evidence pack.
How it compares
What each tool does today, from its own site and docs.
| Capability | Guardyx | Composio | Mintive (formerly MintMCP) | Runlayer | Docker MCP Gateway |
|---|---|---|---|---|---|
| Approvals enforced in the gateway, no agent code | Yes | Partial | Yes | Partial | No |
| Hash-chained audit log | Yes | No | Partial | No | No |
| Connectors + governance on one bill | Yes | Yes | Yes | Not stated | No |
| Works with Claude Desktop / Cursor over MCP OAuth 2.1 | Yes | Partial | Yes | Yes | No |
| Unlimited agents on the free plan | Yes | Not stated | No | Not stated | Not stated |
| Start self-serve, no sales call | Yes | Yes | Partial | No | Yes |
| Free tier | Yes | Yes | No | Not stated | Yes |
Approvals enforced in the gateway, no agent code
- Guardyx
- Yes
- Composio
- Partial
- Mintive (formerly MintMCP)
- Yes
- Runlayer
- Partial
- Docker MCP Gateway
- No
Hash-chained audit log
- Guardyx
- Yes
- Composio
- No
- Mintive (formerly MintMCP)
- Partial
- Runlayer
- No
- Docker MCP Gateway
- No
Connectors + governance on one bill
- Guardyx
- Yes
- Composio
- Yes
- Mintive (formerly MintMCP)
- Yes
- Runlayer
- Not stated
- Docker MCP Gateway
- No
Works with Claude Desktop / Cursor over MCP OAuth 2.1
- Guardyx
- Yes
- Composio
- Partial
- Mintive (formerly MintMCP)
- Yes
- Runlayer
- Yes
- Docker MCP Gateway
- No
Unlimited agents on the free plan
- Guardyx
- Yes
- Composio
- Not stated
- Mintive (formerly MintMCP)
- No
- Runlayer
- Not stated
- Docker MCP Gateway
- Not stated
Start self-serve, no sales call
- Guardyx
- Yes
- Composio
- Yes
- Mintive (formerly MintMCP)
- Partial
- Runlayer
- No
- Docker MCP Gateway
- Yes
Free tier
- Guardyx
- Yes
- Composio
- Yes
- Mintive (formerly MintMCP)
- No
- Runlayer
- Not stated
- Docker MCP Gateway
- Yes
Sources, checked 28 Oct 2026
- Composio: https://docs.composio.dev/docs/approvals.md
- Mintive (formerly MintMCP): https://www.mintive.com/docs/tool-approval
- Runlayer: https://docs.runlayer.com/platform-policies
- Docker MCP Gateway: https://docs.docker.com/reference/cli/docker/mcp/gateway/run/
- Composio: https://composio.dev/content/ai-agent-governance
- Mintive (formerly MintMCP): https://www.mintive.com/docs/security/audit-observability
- Runlayer: https://www.runlayer.com/mcp-gateway
- Docker MCP Gateway: https://docs.docker.com/ai/mcp-catalog-and-toolkit/mcp-gateway/
- Composio: https://composio.dev/pricing
- Mintive (formerly MintMCP): https://www.mintive.com/docs/intro
- Runlayer: https://docs.runlayer.com/platform-connectors
- Composio: https://composio.dev/claude
- Mintive (formerly MintMCP): https://www.mintive.com/docs/cursor-setup
- Runlayer: https://docs.runlayer.com/connecting-clients
- Mintive (formerly MintMCP): https://www.mintive.com/pricing
- Mintive (formerly MintMCP): https://www.mintive.com/
- Docker MCP Gateway: https://www.docker.com/pricing/
Using it at work?
Invite teammates and your workspace grows in place: same tenant, same audit chain, no migration. Paid plans add unlimited teammates, 90 days of searchable history, metering you can bill from, and SSO/SAML/SCIM. Enterprise adds self-hosting in your VPC, bring-your-own connectors and MCP servers, and regulator-ready exports.
Start free in your browser.
Every AI action passes through Guardyx.
5,000 tool calls a month through Guardyx, every governance feature, connectors included, up to 3 teammates. No card, no expiry.