Guardyx for Customer Support
Let support agents actually resolve things, without leaking data or promising what you can’t deliver.
The scenario
AI agents are working the front line now. They answer customers, issue refunds and credits, update accounts, and act on a customer’s behalf. Often, they close cases end to end with no human reviewing every ticket.
Approval requested
Held for a human before it runs.
- Agent
- Support Bot
- Tool
STRIPE_CREATE_REFUND
Arguments
{
  "customer": "cus_Q4mX…",
  "amount": 185000,
  "currency": "usd",
  "reason": "requested_by_customer"
}
Policy
A refund over the $500 support limit: approval required.
Approved. The refund is issued, and your decision is on the audit trail.
Denied. No money moved, and your decision is on the audit trail.
What can go wrong
A support agent shows one customer another customer’s personal data: that’s a privacy incident with regulatory teeth. It hands out a refund or credit outside policy. It makes a promise it can’t keep (“sure, we’ll waive that fee forever”). Or it does something destructive to the wrong account. Every one of these lands on a real person, in real time.
Who owns this problem
Your Head of Support or CX owns this day-to-day. Your CISO or privacy owner is accountable for keeping customer data from walking out through an automated channel.
What it looks like deployed
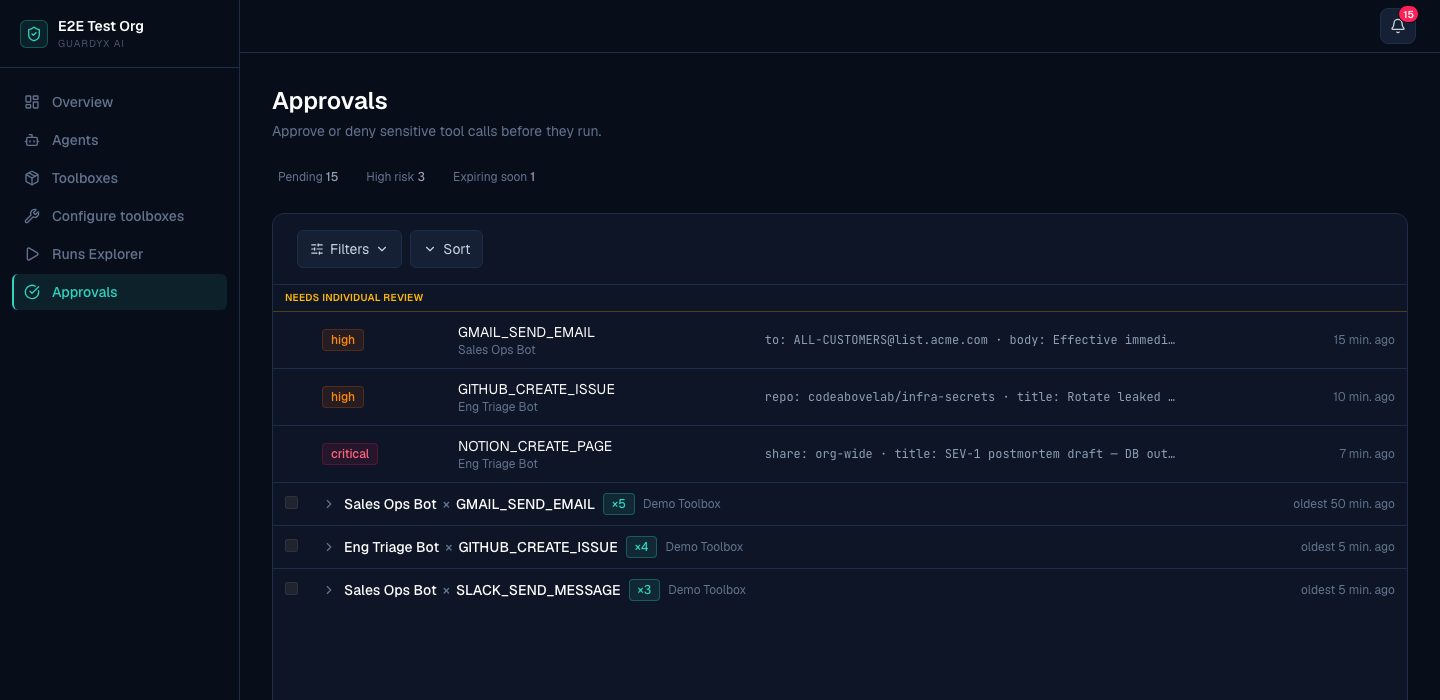
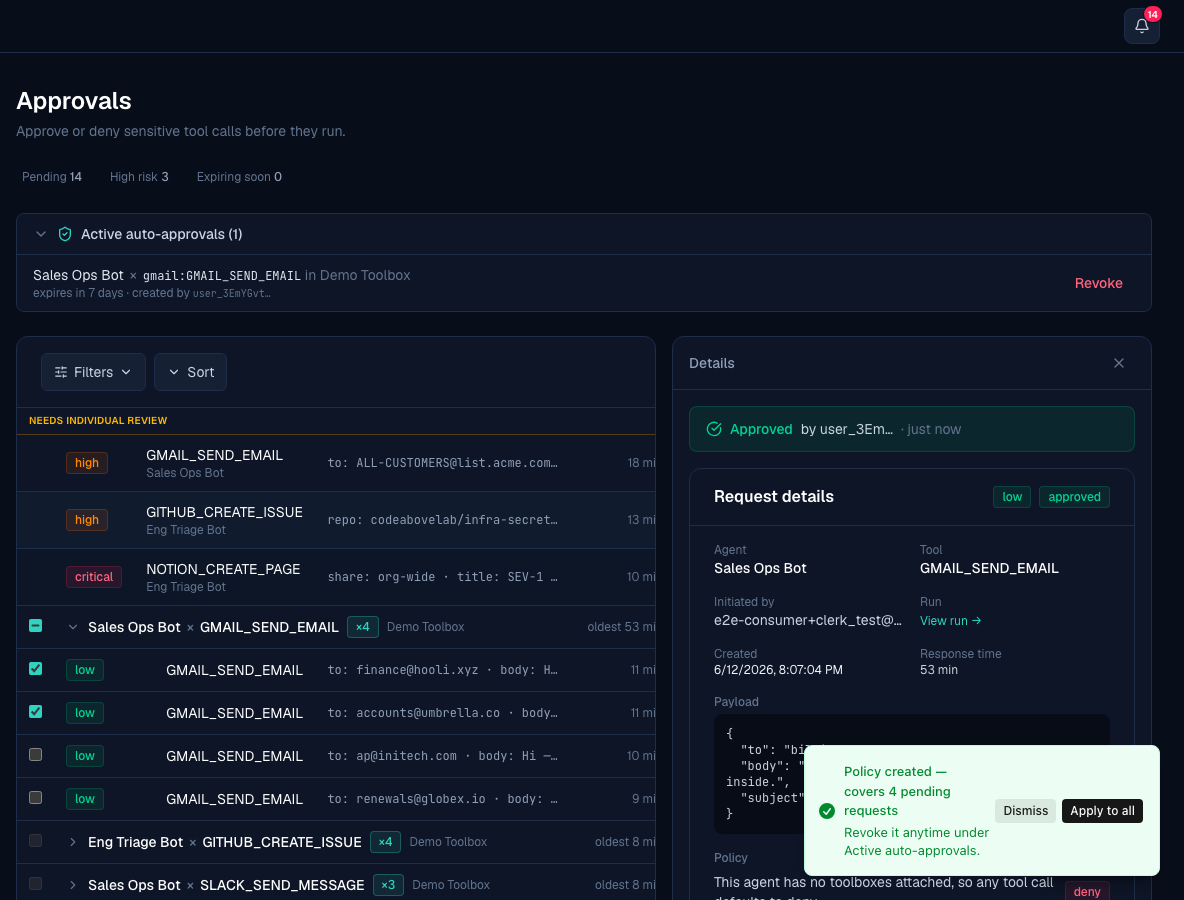
Guardyx sits in front of every action a support agent takes. Answering questions and low-risk fixes just flow. Anything sensitive (sharing account data, a refund over a threshold, changing or closing an account, bending a policy) gets checked and held for a human before it happens. It all gets recorded.
What you're covering
You get a guarantee that no agent leaks data or gives away the store outside policy. Your team doesn’t have to read every ticket to check. Agents handle the routine volume; a human only sees the cases that carry privacy, money, or promise risk.
How it fits your existing tools
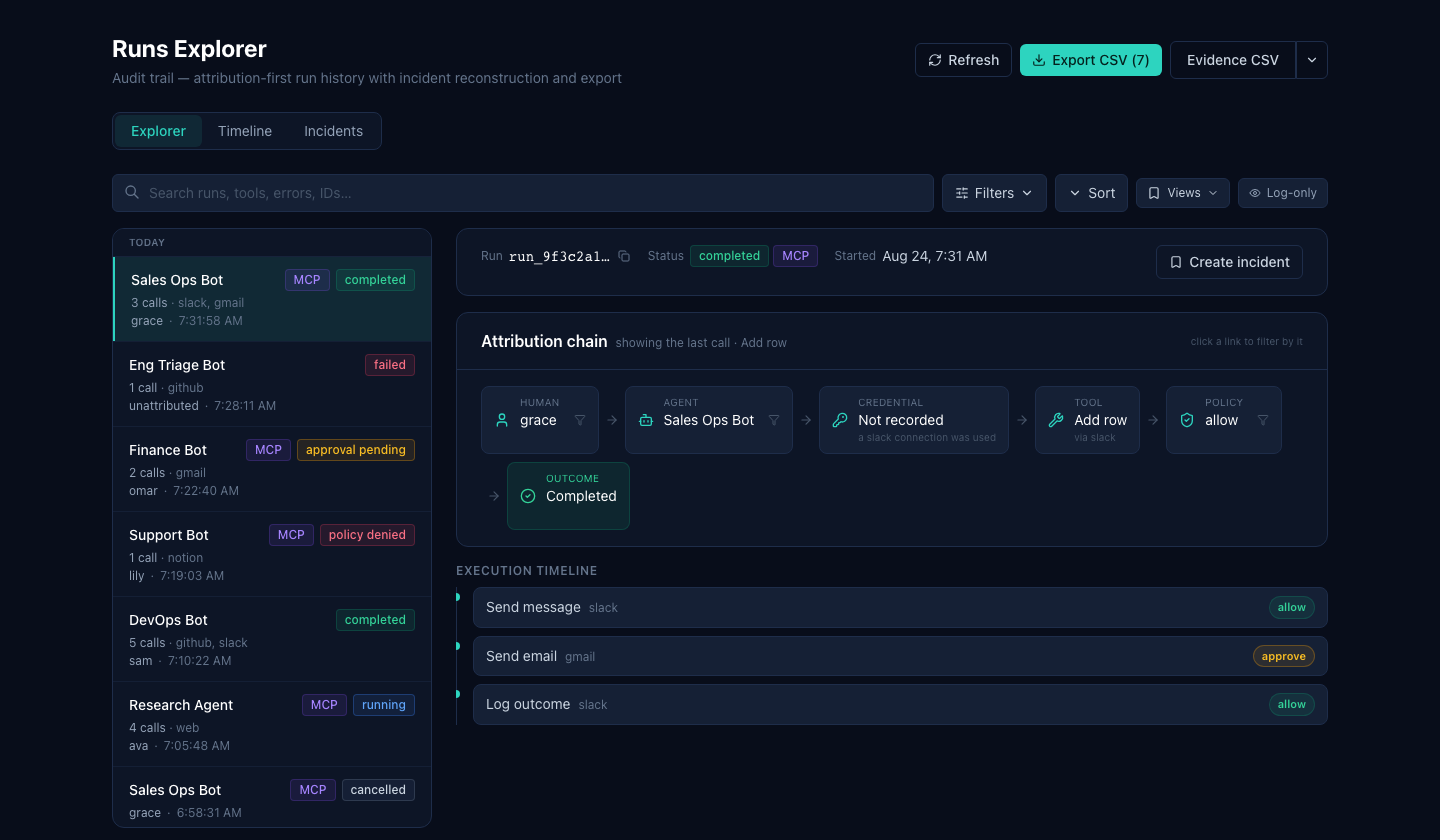
Approvals land in the Guardyx portal, Slack, or email, wherever your support team already works. Every decision is captured as an exportable, auditor-ready evidence pack. You decide what’s sensitive, what the refund limits are, and which actions always need a human. Exceptions are handled cleanly, so customers aren’t left hanging.
Example controls
A quick, plain-language picture of the policy decisions you'd set:
- Allow
- Answering questions and low-risk resolutions.
- Hold for a human
- A refund or credit over your threshold, an account change, or a policy exception.
- Deny
- Disclosing another customer’s data, or a destructive action on the wrong account.
Without Guardyx / With Guardyx
Without: A privacy slip or a bad concession lands on a real customer.
With Guardyx: Sensitive disclosures and over-threshold refunds are held first.
Without: Agents either play it too safe or quietly overstep.
With Guardyx: Routine resolutions flow; risky actions need a human.
Without: Incidents turn up after the fact.
With Guardyx: Every allow / hold / deny is logged.
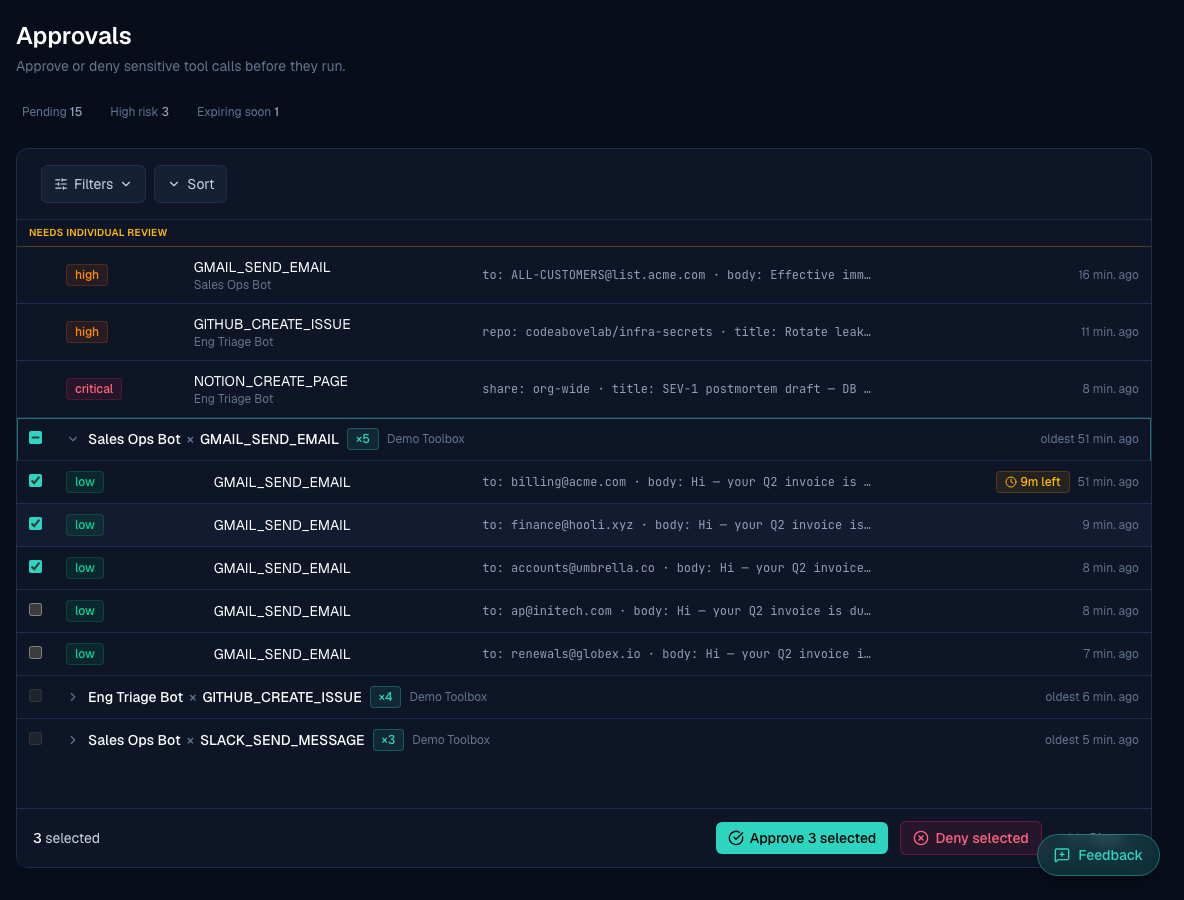
A check on every customer-facing support action.
Refunds and credits over your threshold, account changes, and policy exceptions: checked before a customer sees them.