Guardyx for Finance Workflows
Let finance agents move fast, just not with the wrong money.
The scenario
AI agents are quietly running a lot of finance ops today. They issue refunds, approve invoices, move funds between accounts, reconcile ledgers, and kick off payouts. Often, nobody reviews each transaction.
Approval requested
Held for a human before it runs.
- Agent
- Finance Bot
- Tool
QUICKBOOKS_CREATE_BILL_PAYMENT
Arguments
{
  "payee": "Northwind Supply (new)",
  "amount": 48000.00,
  "currency": "USD"
}
Policy
A brand-new payee: approval required.
Approved. The payment runs now, and your decision is on the audit trail.
Denied. The money never moved, and your decision is on the audit trail.
What can go wrong
In finance, a wrong move is money out the door. An agent misreads a request and issues a refund to the wrong account. It waves through a duplicate or fraudulent invoice. It starts a transfer that quietly breaks an internal control or a regulatory limit. Any one of those is a real loss, a control failure, and (if you’re regulated) something you have to report. Now multiply that by the volume an agent handles. That’s why this keeps people up at night.
Who owns this problem
Your CFO owns the controls at stake. Your Head of Finance Ops runs the day-to-day process. Your CISO has to be able to say that no automated system moves money outside policy.
What it looks like deployed
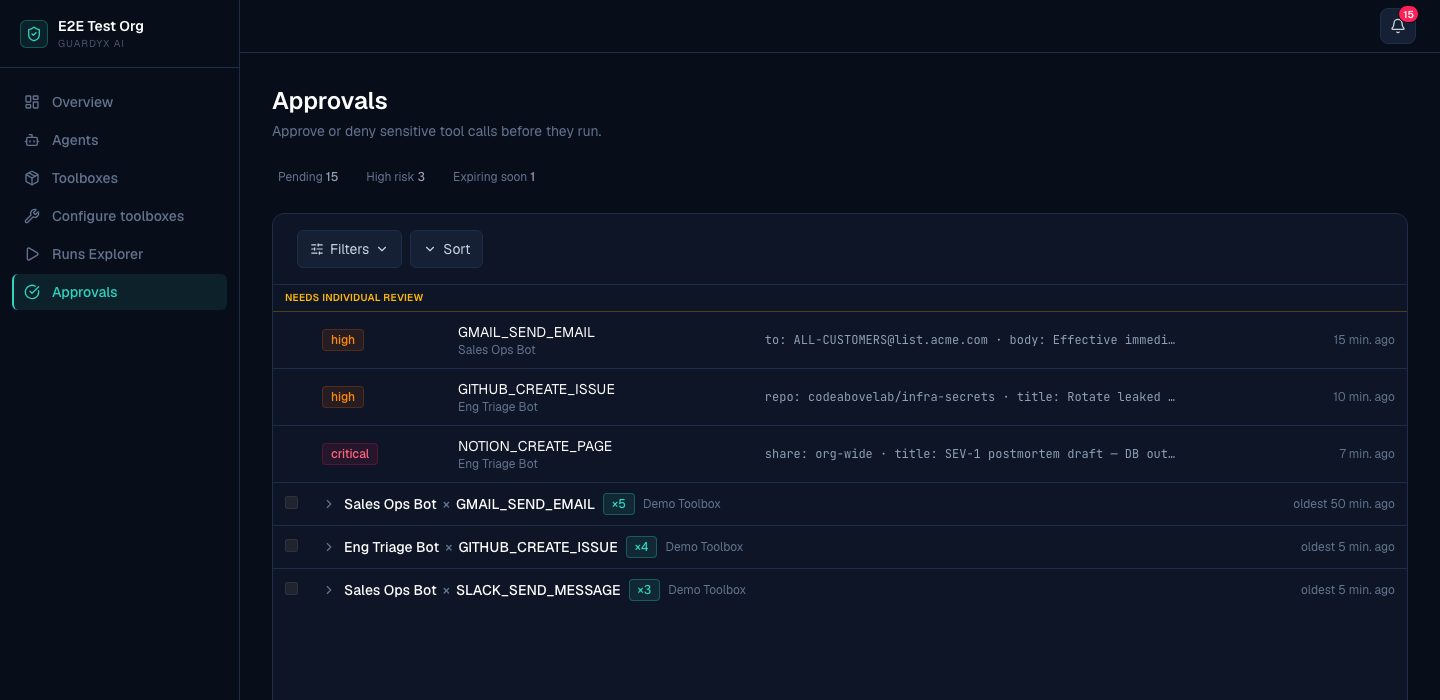
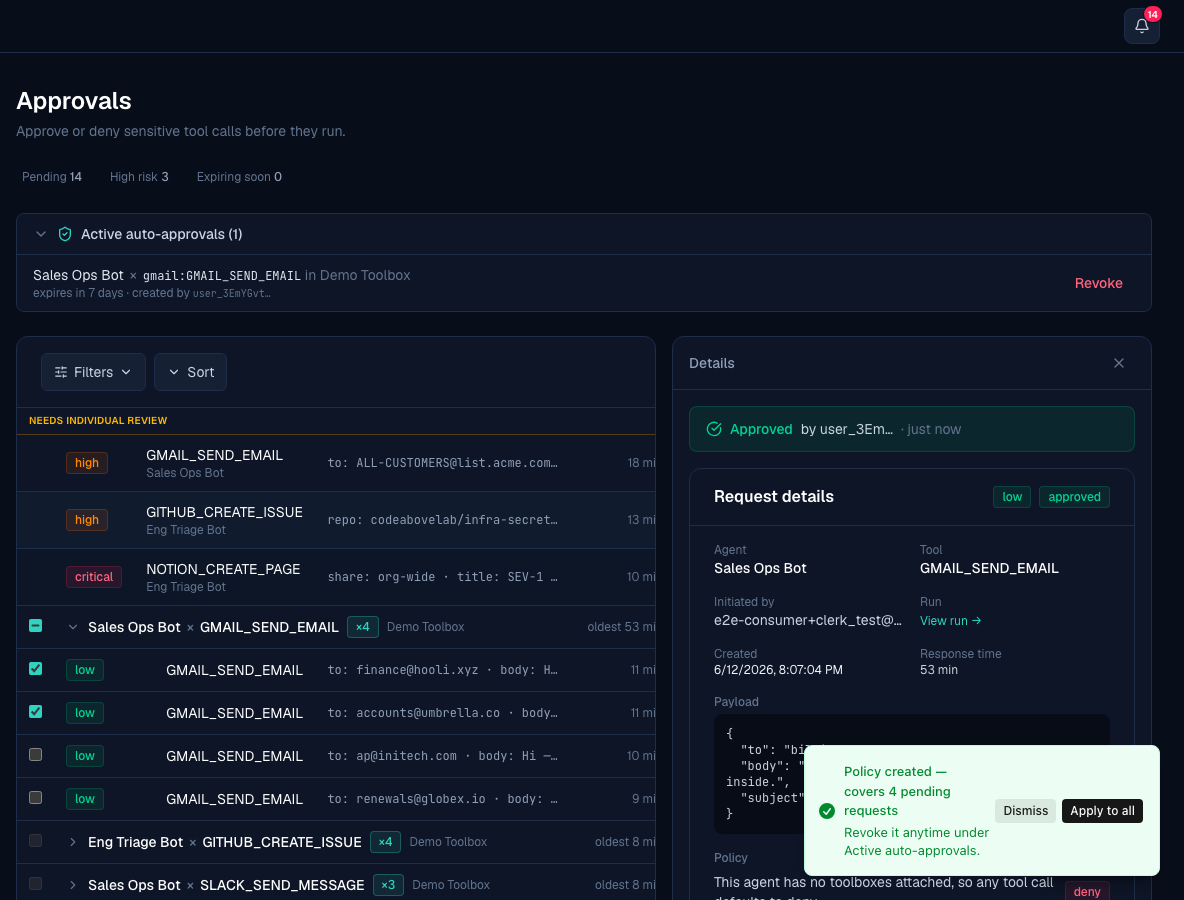
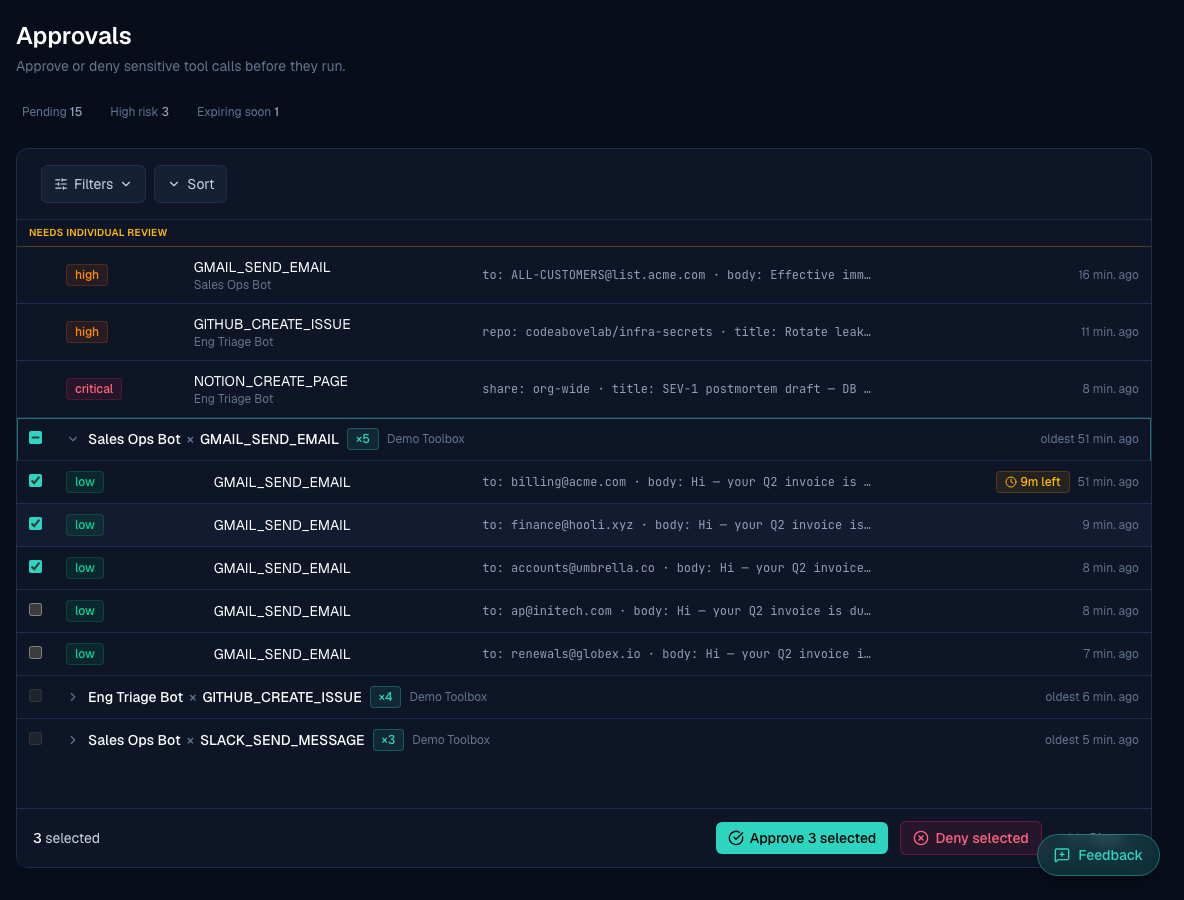
Guardyx sits in front of every financial action your agents take. The small, in-policy stuff (a refund within limits, a pre-approved vendor payment) just goes. Anything that crosses a line (a big amount, a brand-new payee, a pattern that looks off) gets held and sent to a human before it happens. Everything, approved or blocked, gets written down.
What you're covering
You get a rock-solid guarantee that no agent moves money outside your rules. Your team doesn’t have to babysit every transaction. Guardyx does the triage, so people only see the calls that actually need a human; everything else is safe by default and fully logged.
How it fits your existing tools
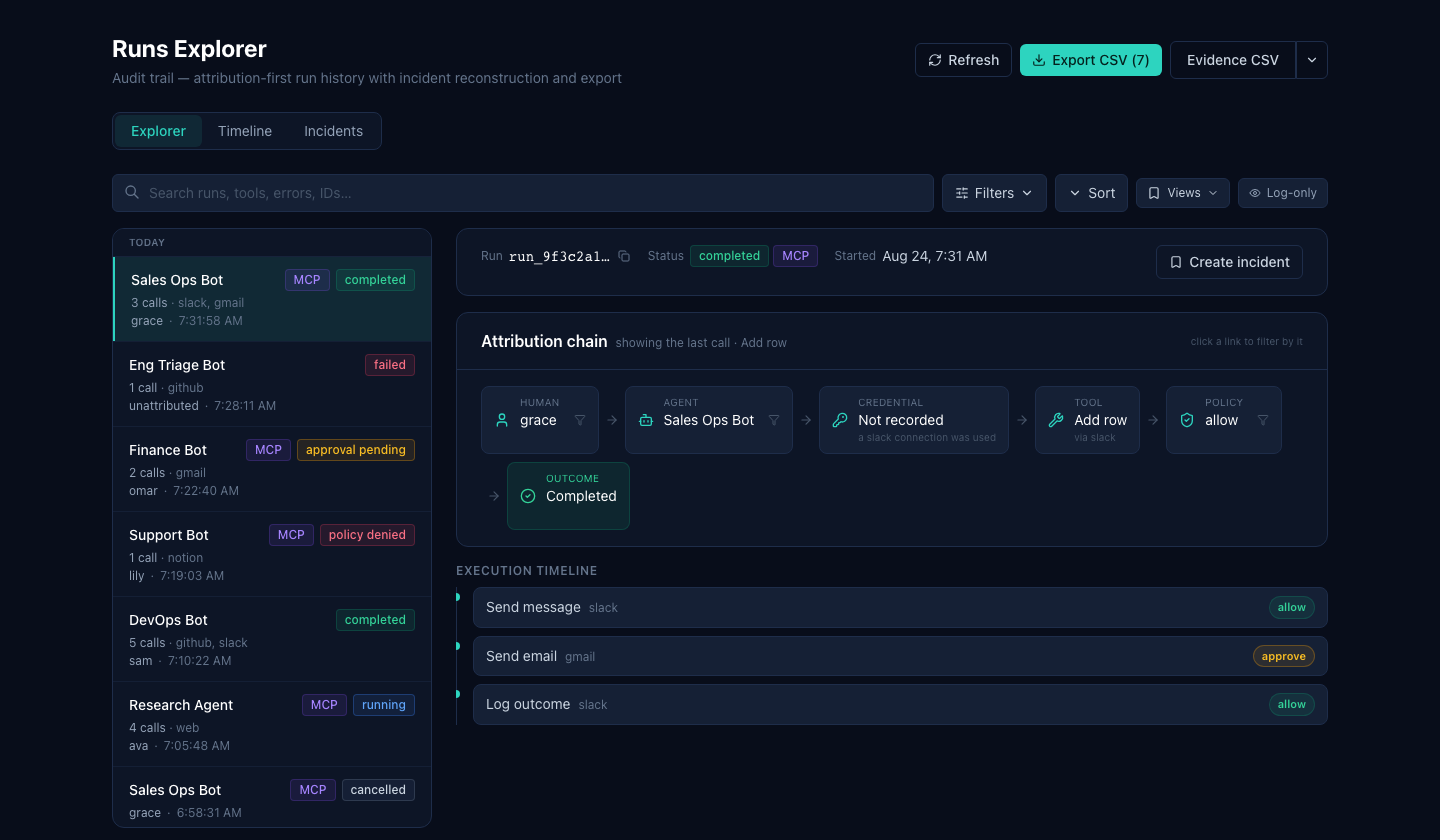
Approvals show up in the Guardyx portal, Slack, or email, wherever your team already works. Every decision, approved or blocked, is captured as an auditor-ready evidence pack you can export. You set the policies and thresholds. Exceptions are handled gracefully, so real work doesn’t get stuck and nobody’s fighting false alarms all day.
Example controls
A quick, plain-language picture of the policy decisions you'd set:
- Allow
- A routine refund below your threshold to an existing customer.
- Hold for a human
- A high-value refund, a brand-new payee, an unusual transfer, or any policy exception.
- Deny
- A prohibited destination, a disallowed account, or anything outside the agent’s authorized scope.
Without Guardyx / With Guardyx
Without: A bad refund or payment shows up after the money’s already gone.
With Guardyx: Out-of-policy payments are held before they execute.
Without: You either trust every transaction or hand-review them all.
With Guardyx: Routine payments flow; only the risky ones need a human.
Without: Reconstructing what happened means digging through logs.
With Guardyx: Every allow / hold / deny is recorded and audit-ready.
A safety net under every finance action.
High-value refunds, brand-new payees, and unusual transfers: held for a human before any money moves.