Guardyx for DevOps Automation
Let agents run your infrastructure, without letting one command take down prod.
The scenario
AI agents are taking on real DevOps and SRE work. They deploy code, change infrastructure and config, manage cloud resources, and respond to incidents, running actual commands against production.
Approval requested
Held for a human before it runs.
- Agent
- DevOps Bot
- Tool
GITHUB_MERGE_A_PULL_REQUEST
Arguments
{
  "repo": "acme/payments-api",
  "pull": 1482,
  "base": "production"
}
Policy
A production change: approval required.
Approved. The merge runs now, and your decision is on the audit trail.
Denied. Production never changed, and your decision is on the audit trail.
What can go wrong
A DevOps agent fires off a destructive command against prod: it deletes a resource, drops a database, or fumbles an access change. You’ve got an outage or data loss in seconds. It might also escalate privileges, disable a security control, or spin up expensive infrastructure it had no business creating. In infra, one wrong automated move hits both uptime and the budget immediately.
Who owns this problem
Your VP of Engineering, Head of Platform, or SRE lead owns this day-to-day. Your CISO is accountable for what changes in production and to security controls.
What it looks like deployed
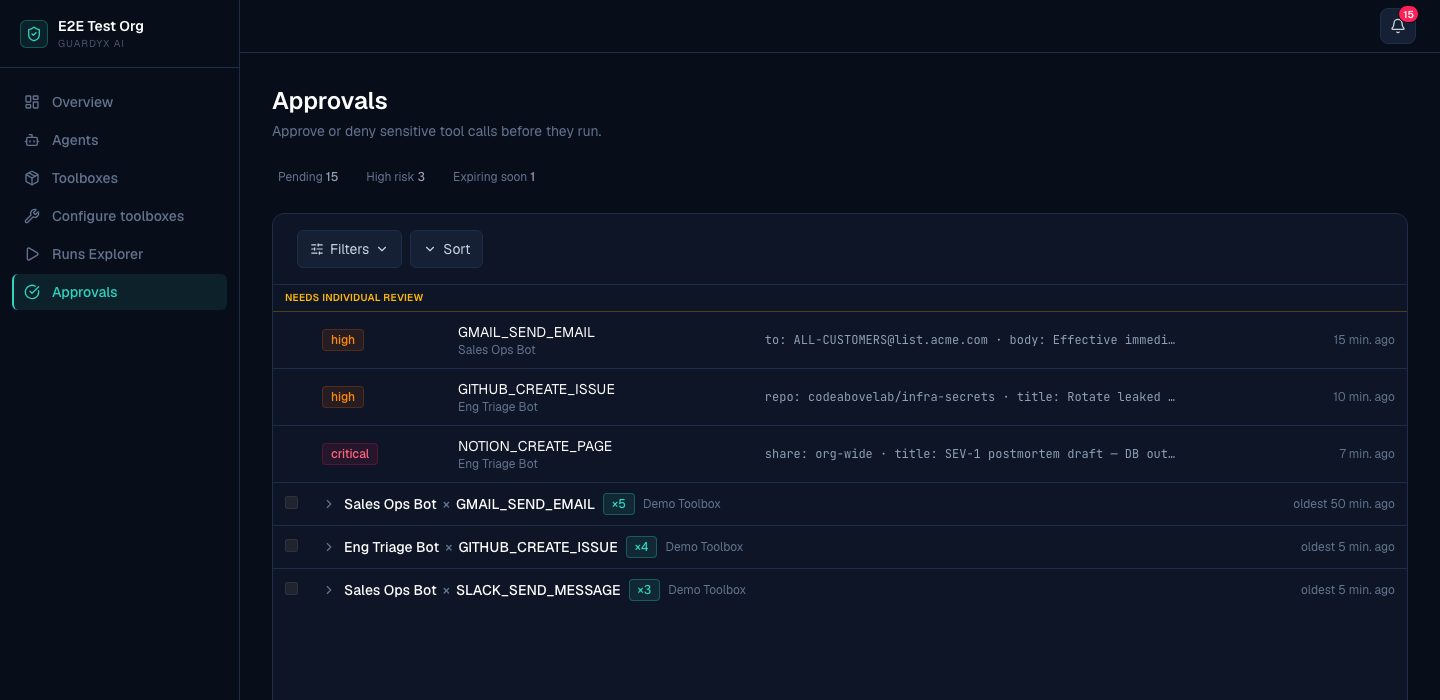
Guardyx sits in front of every action a DevOps agent takes. The safe, in-policy stuff runs on its own. The scary stuff (destructive commands, production changes, privilege or security-control tweaks) gets checked and held for a human before it runs. Every command is logged.
What you're covering
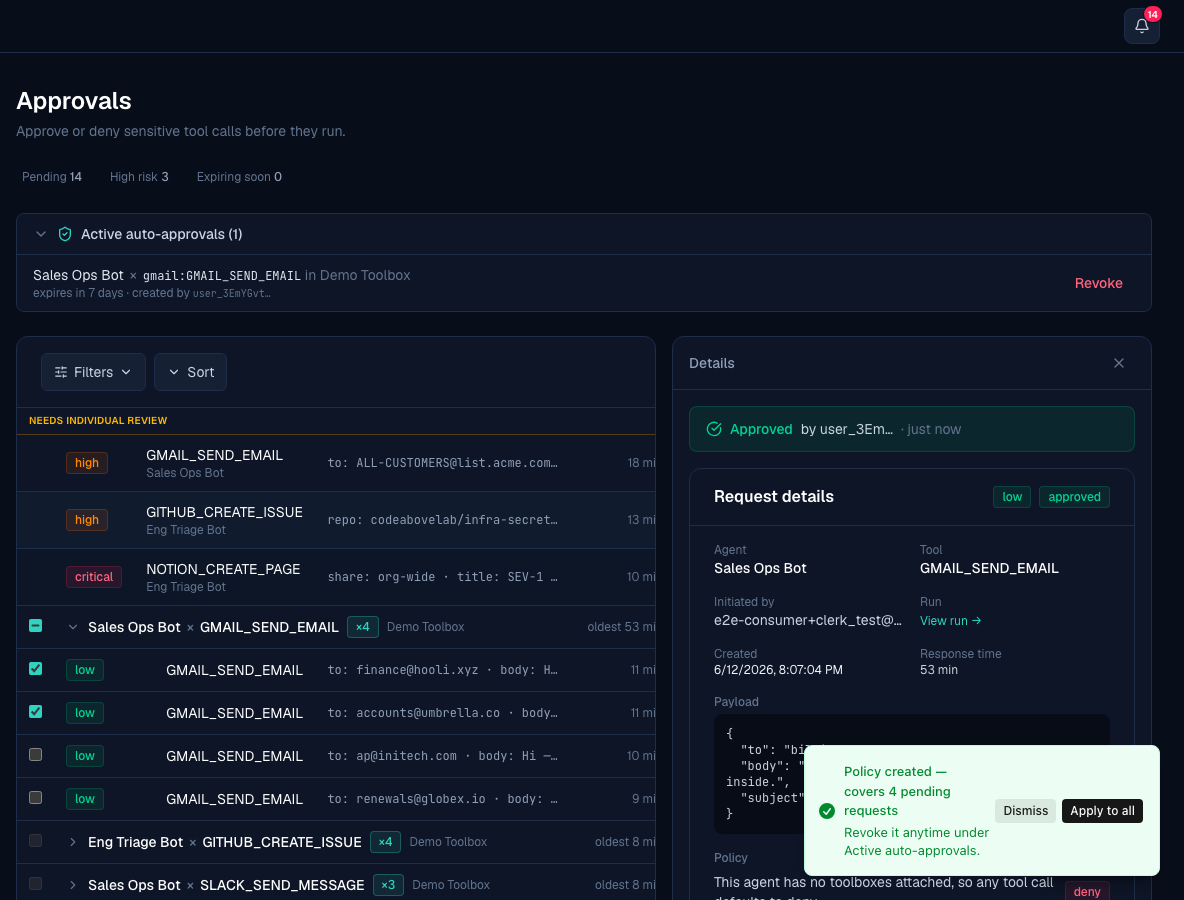
You get a hard stop on dangerous commands reaching prod without a human. You don’t have to turn off automation or review every routine task by hand. Agents carry the safe operational load; your engineers only weigh in on the handful of actions that could actually break something.
How it fits your existing tools
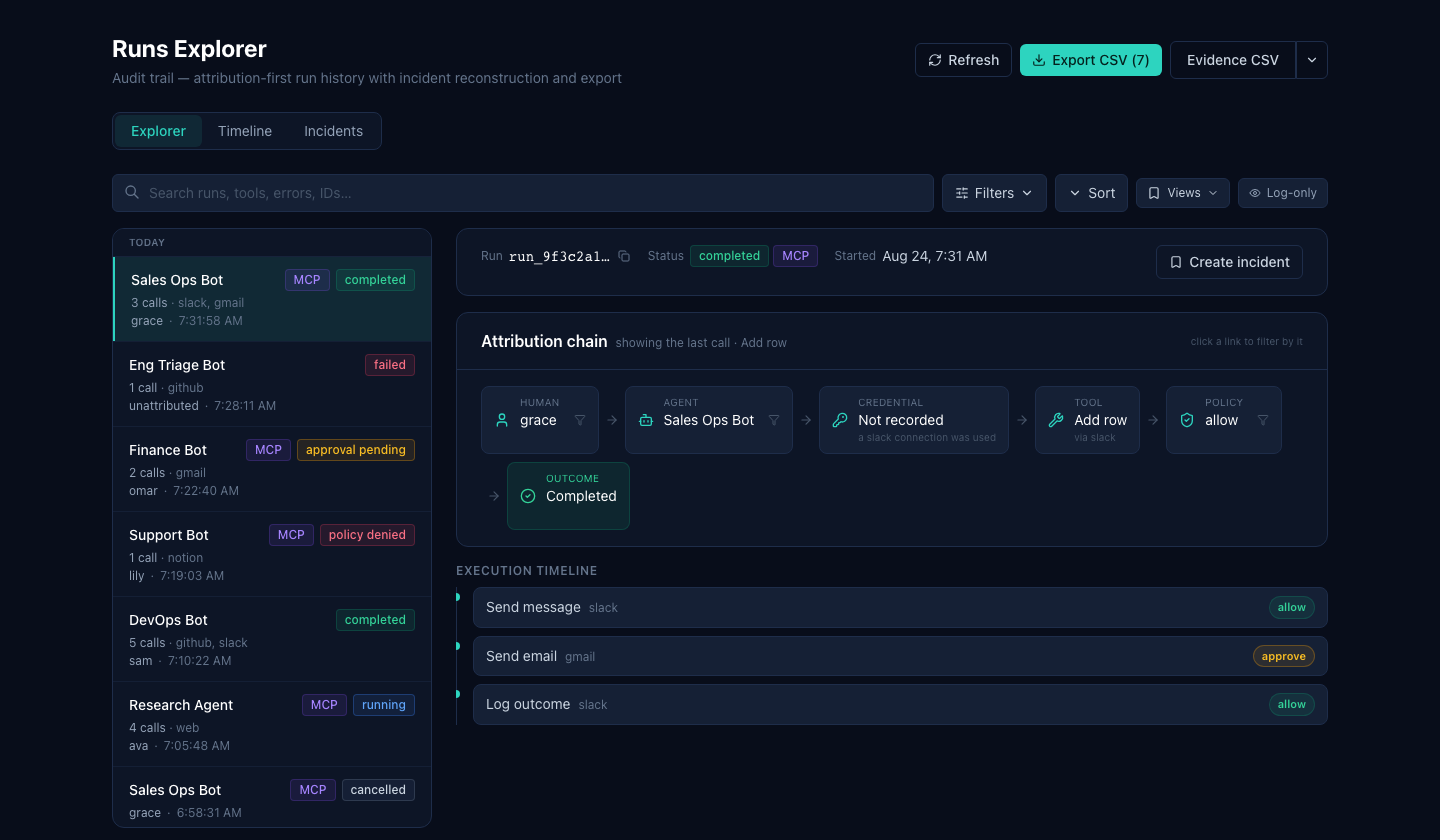
Approvals show up in the Guardyx portal, Slack, or email, wherever your on-call team already works. Every command is captured as an exportable, auditor-ready evidence pack. You decide what counts as high-risk, which environments need a sign-off, and how emergencies get handled. Exception paths keep incident response from ever slowing down.
Example controls
A quick, plain-language picture of the policy decisions you'd set:
- Allow
- Safe, in-policy operations (non-prod deploys, read-only checks).
- Hold for a human
- Production changes, privilege changes, or spinning up costly resources.
- Deny
- Destructive commands, disabling a security control, or touching an out-of-scope environment.
Without Guardyx / With Guardyx
Without: One destructive command can take down prod in seconds.
With Guardyx: High-risk commands are held for a human before they run.
Without: You either slow everything down or risk everything.
With Guardyx: Safe ops run automatically; only risky ones need approval.
Without: Change history is scattered across systems.
With Guardyx: Every command is recorded and reviewable.
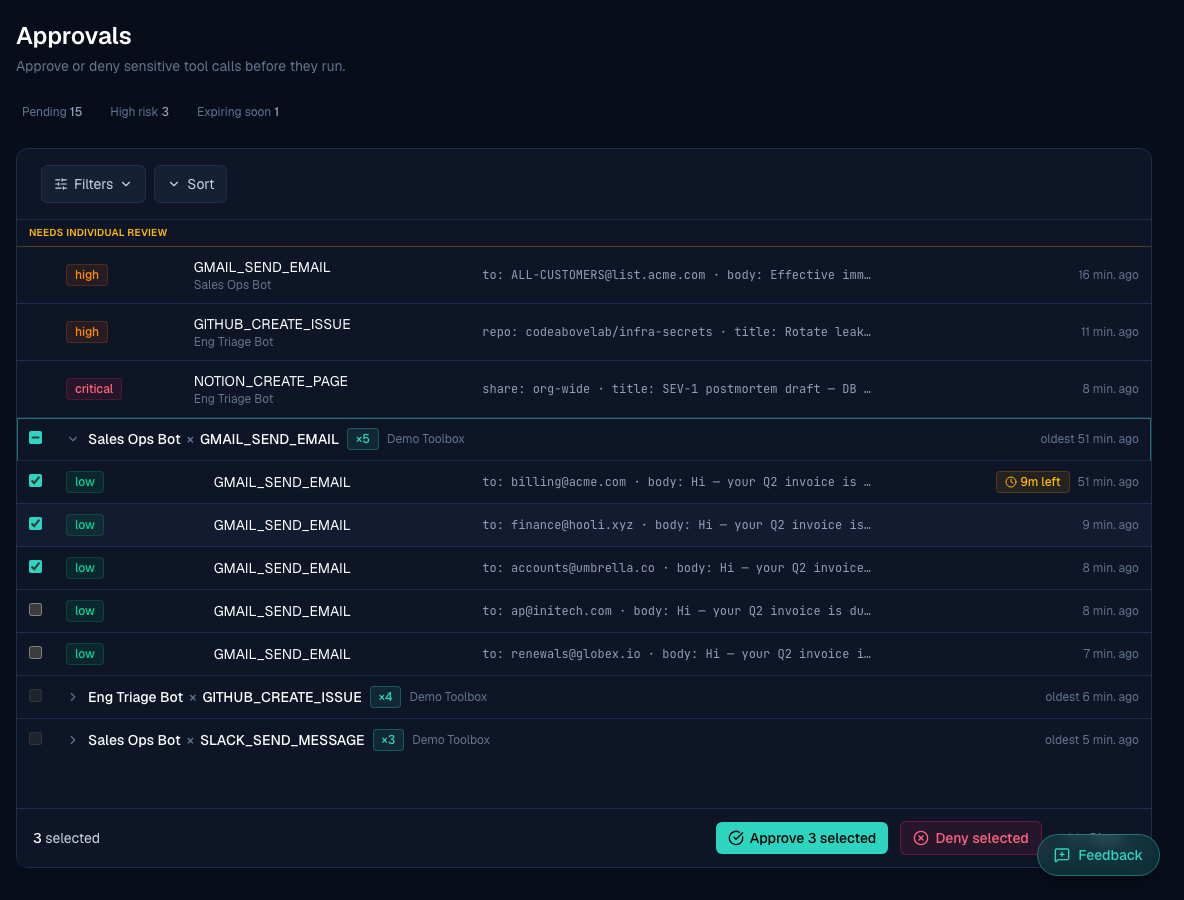
A sign-off before every production change.
Production changes, privilege changes, and costly resources: a hard stop before anything reaches prod.