Guardyx for Legal & Contract Workflows
Let legal agents draft, review, and act, without committing the company to something nobody signed off on.
The scenario
AI agents are showing up in legal and contract work. They review and redline contracts, answer questions from the clause library, draft NDAs and vendor agreements, and flag risk. In some setups, they also send documents out or route them for signature.
Approval requested
Held for a human before it runs.
- Agent
- Contracts Agent
- Tool
DOCUSIGN_SEND_ENVELOPE
Arguments
{
  "document": "MSA — Initech (redlined v3)",
  "to": "legal@initech.com",
  "action": "sign"
}
Policy
Routing a document to an external party for signature: approval required.
Approved. The envelope goes out, and your decision is on the audit trail.
Denied. Nothing was sent for signature, and your decision is on the audit trail.
What can go wrong
In legal, a wrong move is a binding or disclosing one. An agent fires off a contract to a counterparty with the wrong terms, or quietly approves language that waives a protection you count on. It shares privileged or confidential material with the wrong person. It signs the company up for an obligation, a price, or a liability no attorney ever looked at. A bad draft is annoying, but these actions carry legal weight, and they’re really hard to walk back.
Who owns this problem
Your General Counsel and legal ops team own this day-to-day. Your CISO is on the hook for keeping privileged and confidential material from slipping out through an automated channel.
What it looks like deployed
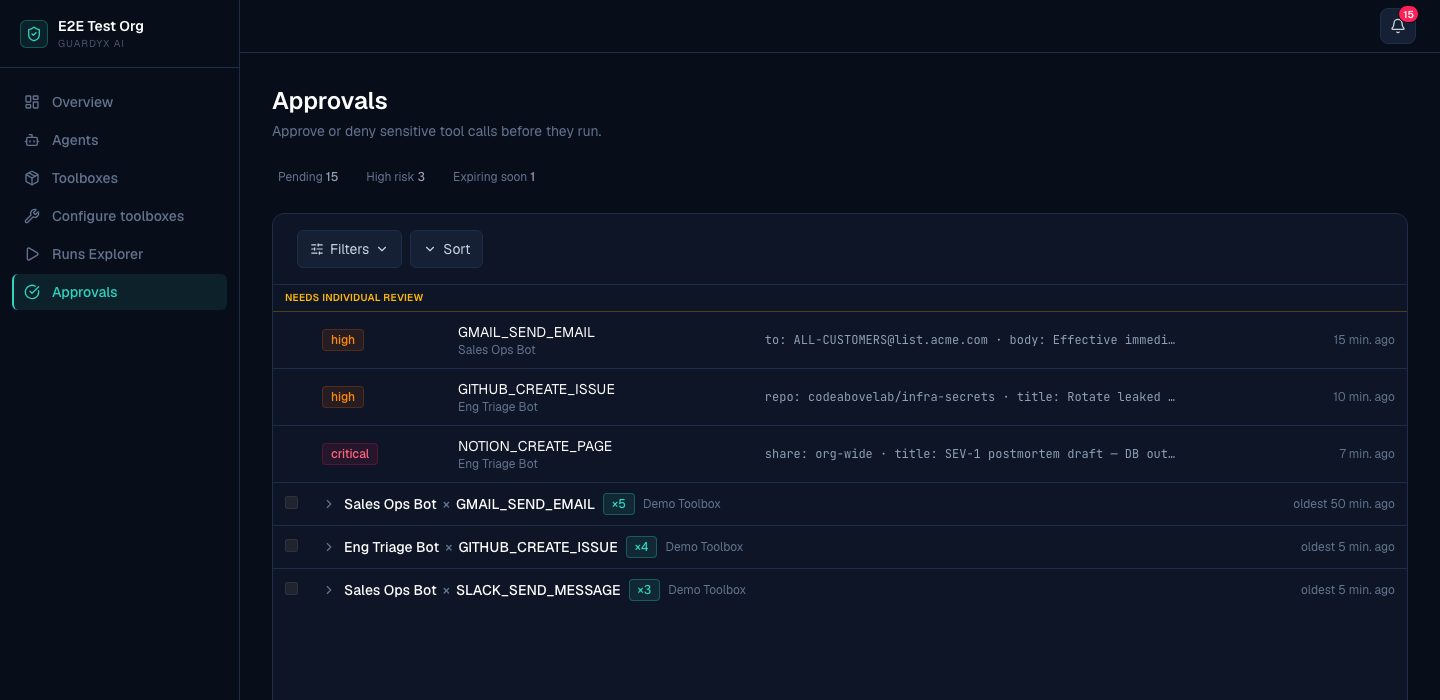
Guardyx sits in front of every action a legal agent takes. Reading, drafting, and internal analysis? Go right ahead. But anything with external or binding effect (sending a document out, approving non-standard terms, routing for signature, reaching into a privileged data store) gets checked against policy and held for an attorney before it happens. All of it, approved or blocked, gets logged.
What you're covering
You get peace of mind that nothing with legal weight goes out the door without a human. Your team doesn’t have to re-read every routine draft to be sure. Guardyx draws the line between “fine to automate” and “get a lawyer on this,” so your attorneys spend their time only where the real risk is.
How it fits your existing tools
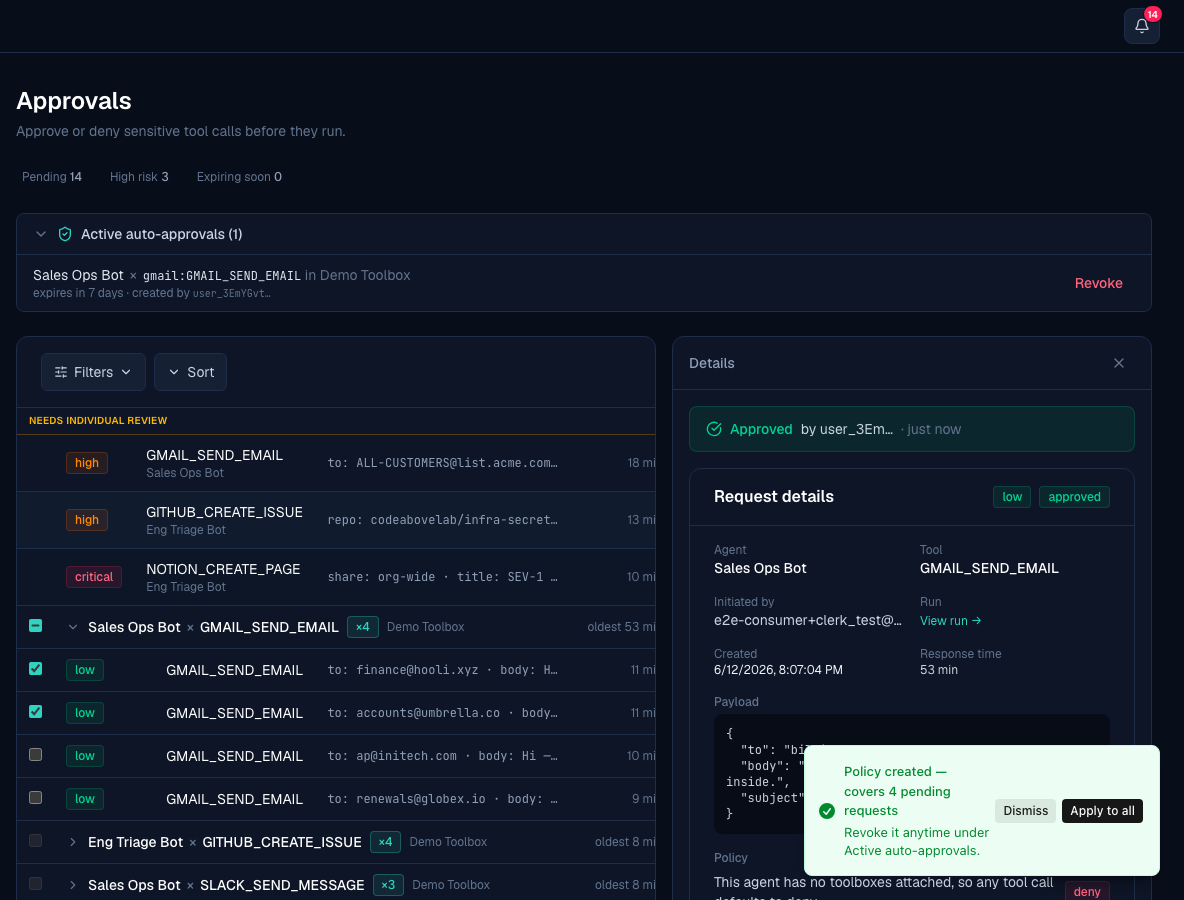
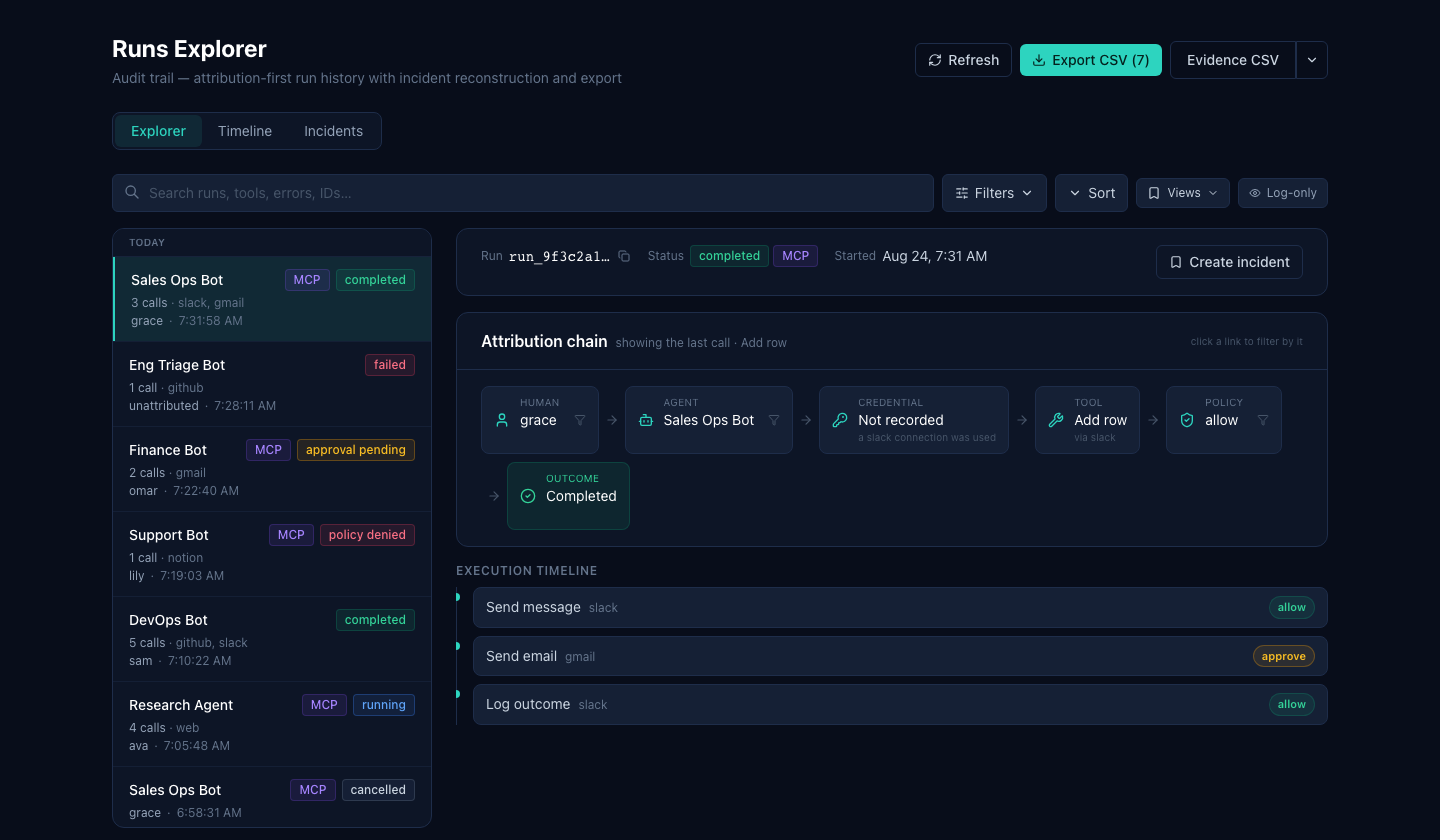
Approvals land in the Guardyx portal, Slack, or email. Every decision is captured as an auditor-ready evidence pack you can export for compliance and records. You decide what counts as non-standard terms, which document types always need a review, and how privileged material gets handled. Exceptions are handled cleanly, so the everyday stuff isn’t stuck waiting.
Example controls
A quick, plain-language picture of the policy decisions you'd set:
- Allow
- Internal drafting, redlining, and clause-library lookups.
- Hold for a human
- Sending a document to an external party, approving non-standard terms, or routing something for signature.
- Deny
- Disclosing privileged material to an unauthorized recipient, or committing to terms outside the approved playbook.
Without Guardyx / With Guardyx
Without: A wrong-term contract or disclosure goes out and can’t be recalled.
With Guardyx: Binding or disclosing actions are held for an attorney first.
Without: Lawyers re-read every routine draft just to stay safe.
With Guardyx: Drafting flows; only external or binding actions need sign-off.
Without: Proving who approved what is a manual scramble.
With Guardyx: Every decision is logged for compliance and records.
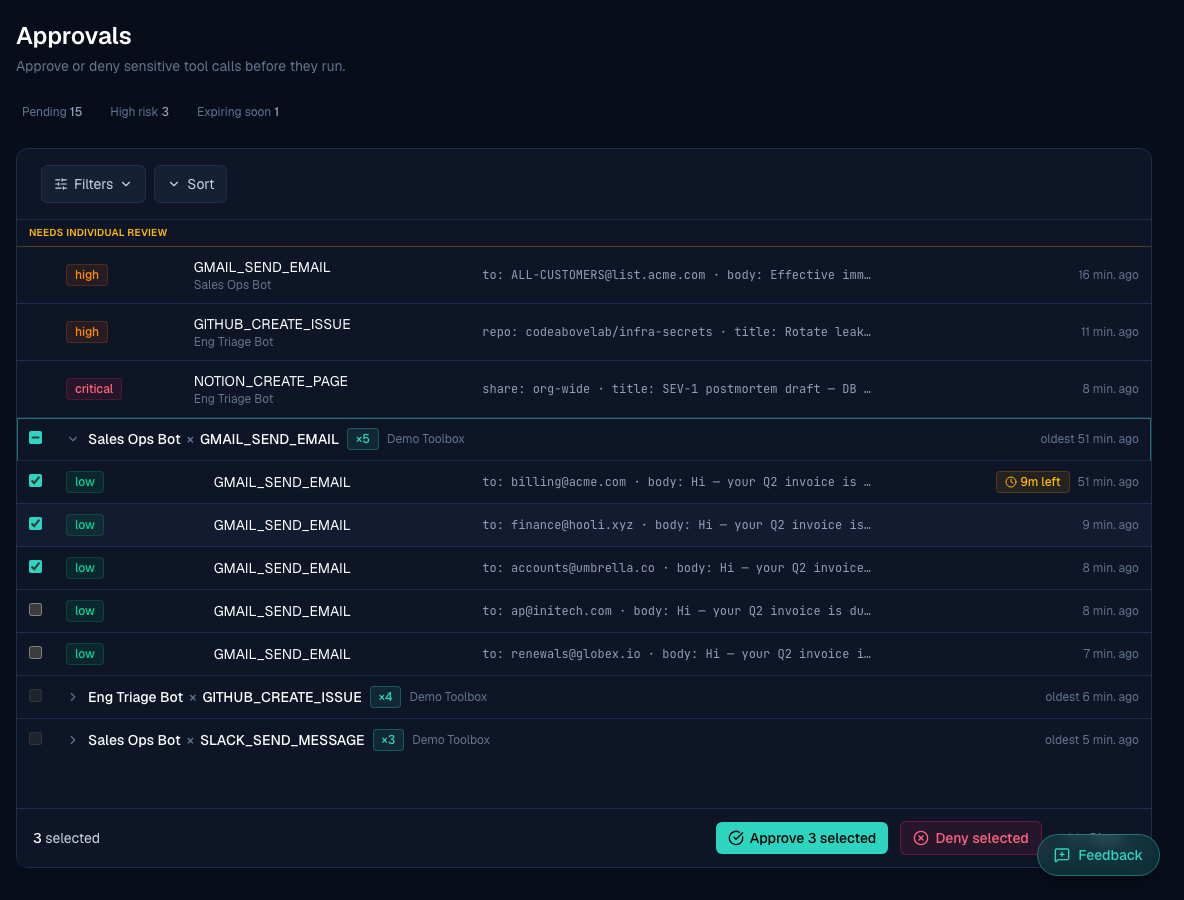
A sign-off before every binding legal action.
Non-standard terms, anything routed for signature, and documents going to an external party: sent to a human first.